If you have a workspace app that requires authorisation, which runs a workspace that makes a http call to the FME Rest API, is it possible to use the logged in user to authenticate the http request?

Using a private Workspace App end user to directly authenticate an API call: The signed-in user's session or token isn't passed to the workspace from the app, so an HTTPCaller can't directly authenticate with the end users tokens.
There may potentially be some creative solutions in FME Form that could meet your needs.
If calling the API as the end user is a hard requirement and there are no solutions that come up, it'd make a good Ideas post.
As mentioned the app doesn’t pass through the users authentication details and getting the session token in app is very yuck and you will be jumping through hoops.
But I think you can do this, by being a bit tricky.
In your workspace that is call by the Flow App, you call make a call with an account with significant rights.
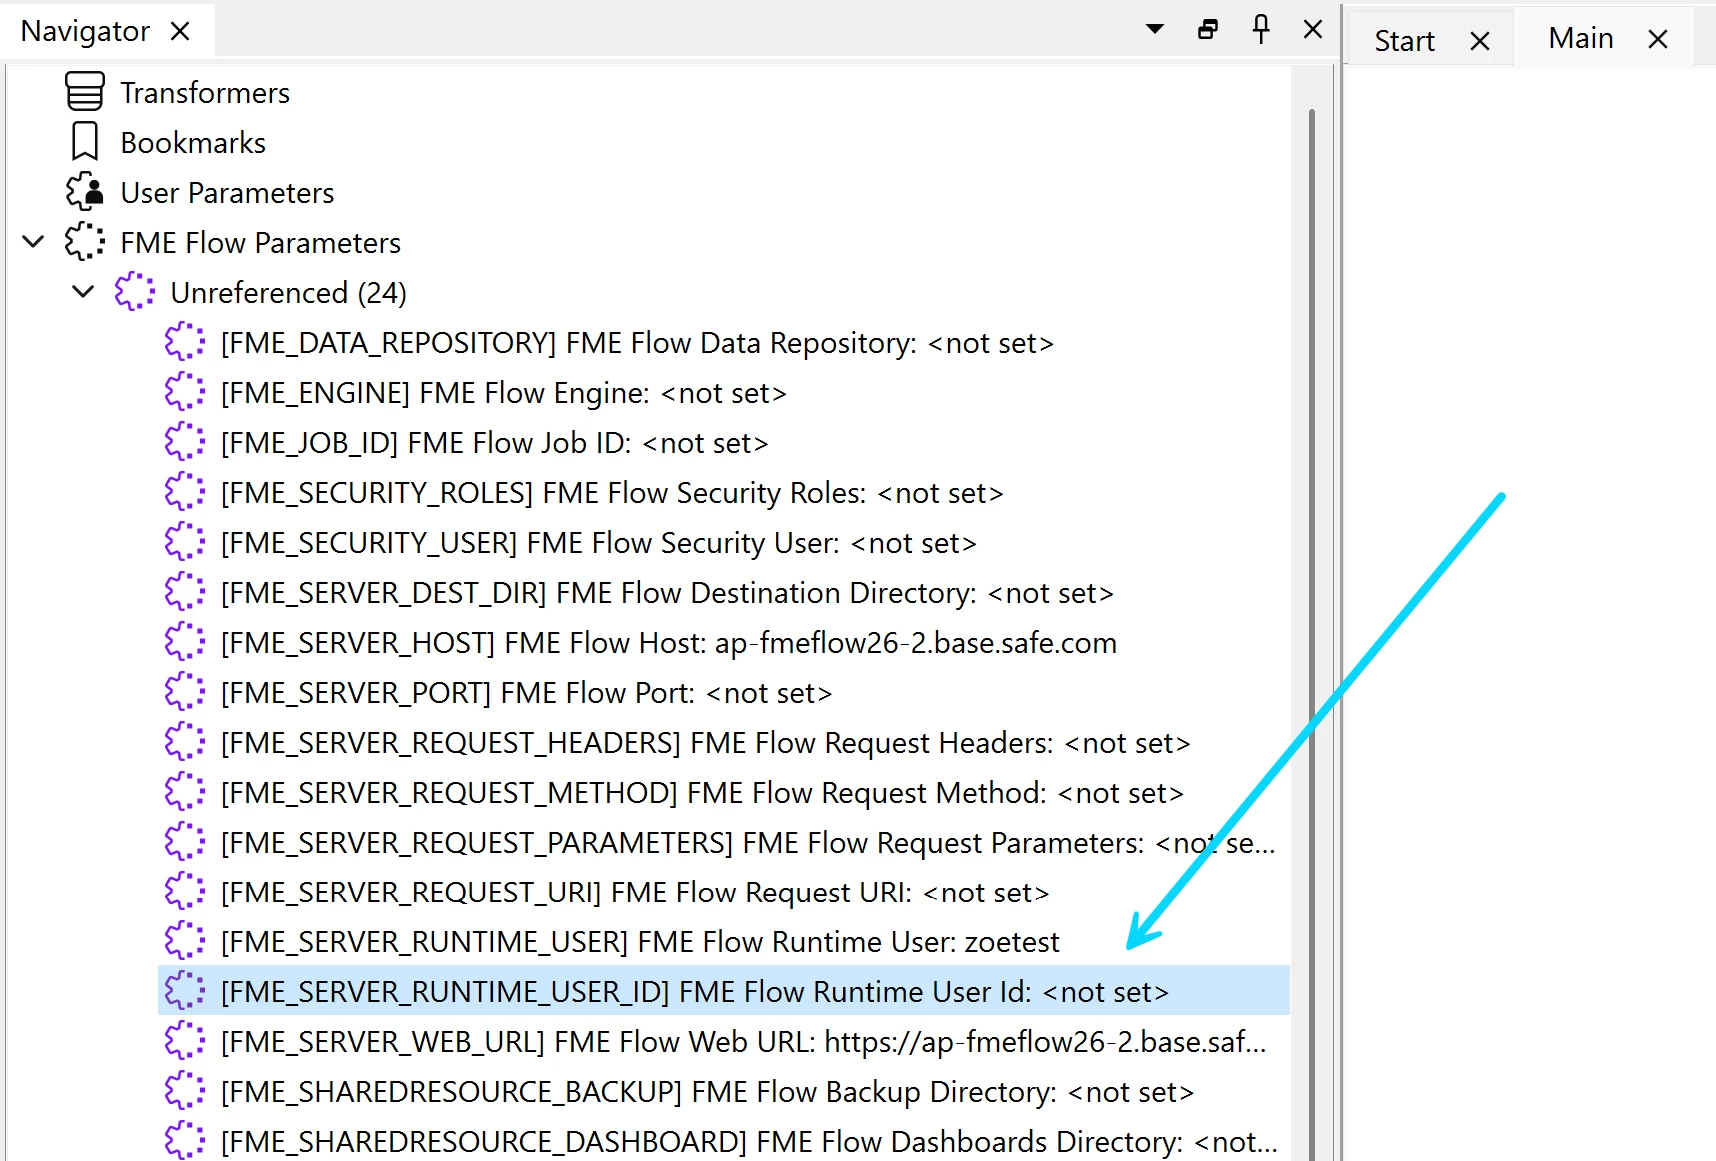
Get the User id based on the Runtime user
Use the User id inside a call to get an FME Flow api token with custompermission = false
That token returned now inherits the permissions of the specific runtime user and appears
Use the token in the call to the Rest API endpoint you are interested in
Then delete the token….API tokens without custom permission should not be left around.
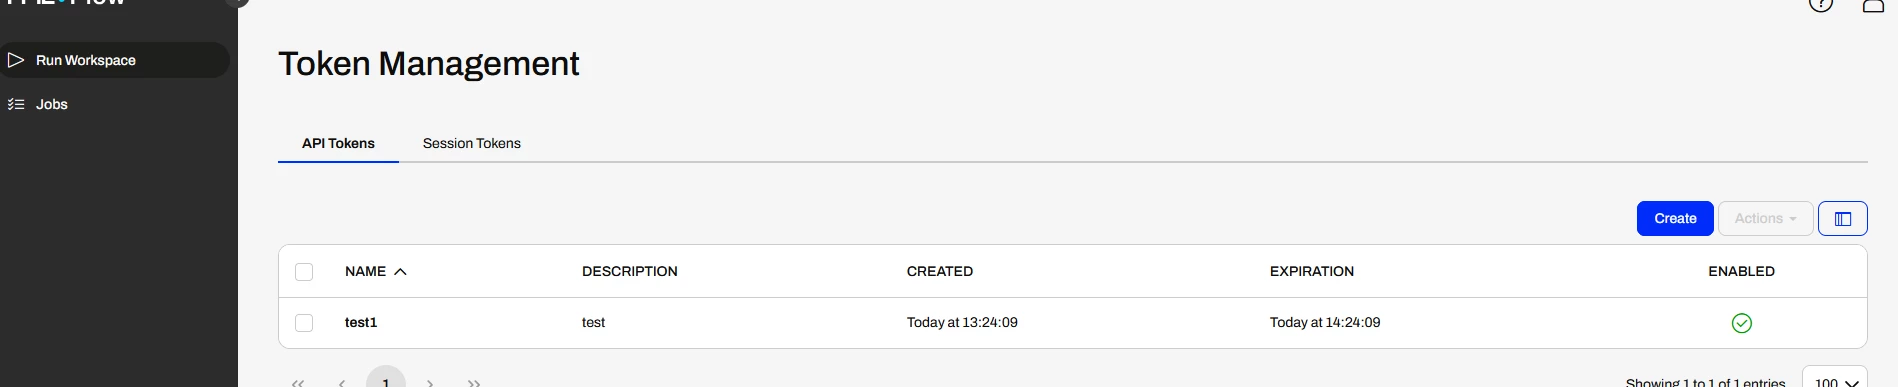
Here is an example of me making a token, using a admin login, to create a token for the guest and what is viewable under the guest login, and it inherits the permissions of what the guest account normally has (not the admins permissions).
Just need to make sure you take any security consiuderations into account.